You open a newsletter on Tuesday at 9:47 in the morning, standing in line for coffee, phone in one hand. You skim it for six seconds and move on with your day.
By 9:48, the sender knows you opened it. They know you opened it at 9:47, from a phone, in Chicago, and that you opened it twice — once in line, once more at your desk. They did not ask. Your email app did not warn you. Nothing on screen indicated that reading an email had become a two-way transmission.
This is not a hack or a data breach. It is a feature, sold openly, used by an enormous share of commercial email. And once you understand how it works, you will never look at a "just checking in!" marketing email the same way again.
The one-pixel spy: how it actually works
A tracking pixel is, mechanically, the simplest surveillance device on the internet. It is an image — usually a 1×1 transparent GIF, invisible to the human eye — embedded in the body of an HTML email. When your email client loads the message's images, it requests that image from the sender's server. That request is the entire trick.
Here is why the request matters: the image URL is unique to you. Not to the campaign — to you. When the company sends a million copies of a newsletter, each copy carries a slightly different pixel URL, tied to your address in their database. The moment your client fetches the image, their server logs the hit against your record. You "opened" the email, as far as their analytics are concerned, because your device asked for the pixel.
No JavaScript runs. No permission is requested. The email format your client renders every day — HTML with remote images — is the whole attack surface. If your client loads images automatically, and most do by default, every marketing email you open phones home.
Five things a single open tells them
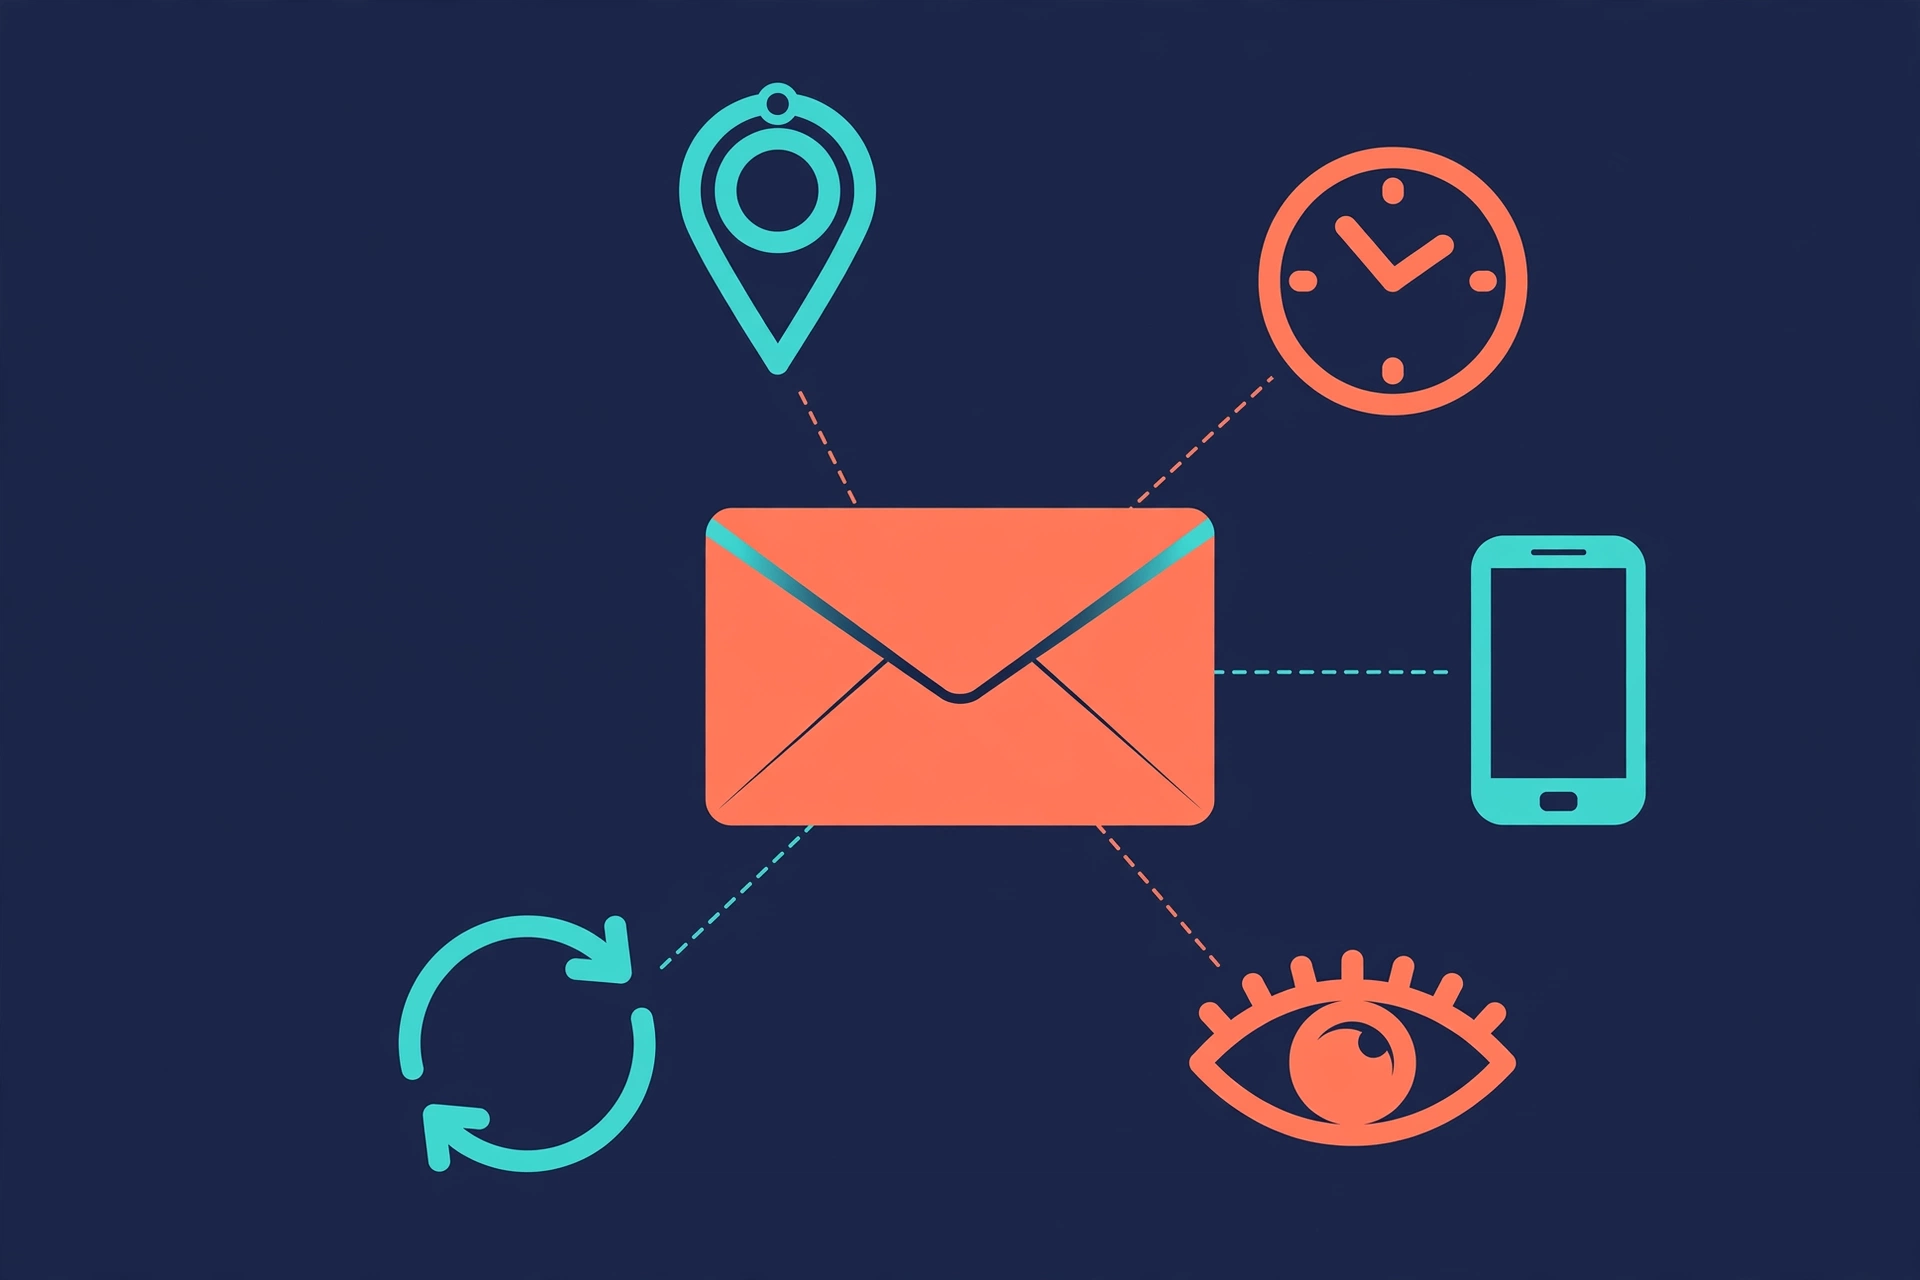
One pixel firing delivers a small dossier. None of it requires you to click anything.
1. Exactly when you opened it. Timestamped to the second. Marketers use this to build "engagement windows" — they learn you read email at 9:47 AM and start scheduling sends for 9:40.
2. Roughly where you are. The image request carries your IP address, which maps to a city-level location in most cases. Open the same newsletter from home and from the office and they can watch the two locations diverge.
3. What device and app you use. The request includes a user-agent string: iPhone or Android, Apple Mail or Gmail app, desktop or mobile. This feeds the "optimize for the device they actually use" playbook.
4. How many times you re-opened it. Every re-open fires the pixel again. Opened it four times before forwarding it to your boss? They know it was interesting. Email analytics dashboards literally show per-recipient open counts.
5. Whether you forwarded it. If the person you forwarded it to opens it, the pixel fires from their IP address and device — a second location and user-agent attached to your record. Some marketers treat this as a feature ("viral forwards!"). Your friend did not consent to be fingerprinted; they just opened an email you sent.
None of this is theoretical. It is the standard analytics panel of every major email marketing platform, most of which ship open tracking switched on by default.
Who's watching: it's not just spammers
The uncomfortable part is who does this. It is not the sketchy "YOU WON" spammer — those usually can't be bothered. It is the legitimate businesses you actually gave your address to: the retailer from that holiday coupon signup, the SaaS tool's onboarding drip, the nonprofit's newsletter, the airline's fare alerts. Open tracking is a default-on feature of the marketing platforms they all use, which means your address entered a tracking database the moment you subscribed, through no decision of your own.
Beyond the sender, there is a second layer: data brokers and list buyers. When a company sells or shares its list — and many do, in the fine print you never read — the behavioral profile attached to your address goes with it. "Opens email within 10 minutes, reads on iPhone, located in Chicago, re-opens pricing emails" is a targeting segment worth money. Your reading habits become inventory.
The big platforms have pushed back, partially. Gmail has routed images through its own proxy servers since 2013, which hides your IP address and location from the sender — though the sender still sees that you opened the message. Apple went further: Mail Privacy Protection, launched with iOS 15 in September 2021, pre-loads remote content privately so senders can't tell when — or even whether — you opened an email in Apple Mail. Both help, but both are client-side band-aids on a protocol-level behavior. The pixel still fires; it just reports less.
Why a temp email is a tracking pixel's worst enemy
Here is where disposable email turns from a spam tool into a surveillance countermeasure. A tracking pixel is only valuable as part of a profile — one open means little; a thousand opens across two years, tied to one address, is a behavioral goldmine. The pixel needs the address to persist. A temp email refuses to.
When you sign up for that newsletter or coupon with a disposable address, the pixel still fires if you open the mail. But the profile it feeds belongs to an address that will be dead in hours or days. The marketer's database accumulates opens against an identity that no longer exists. The data broker who buys the list gets a row of behavioral data pointing at a void. Retargeting built on that address — the "we saw you opened our email" ad campaigns — targets nobody.
This is the asymmetry that makes temp mail so effective here: the tracking infrastructure assumes permanence, and you simply decline to provide it. You don't need to block the pixel. You just need to make sure the thing it reports back about isn't you.
It also solves the consent problem cleanly. That "unsubscribe" link at the bottom of spam you never signed up for? Clicking it confirms to the sender that your address is live and monitored — the worst possible response to unsolicited mail. With a temp address, there is nothing to unsubscribe from. The address dies, and the entire relationship — pixels, profiles, and all — dies with it.
The pixel-killing stack: four layers
A temp email is the strongest single move, but the complete defense has four layers. I run all four, and none of them costs anything or takes more than a few minutes to set up.
Layer 1: Temp email for every signup you don't trust. Newsletters, coupons, downloads, trials — anything where the address is the price of admission gets a disposable address. This is the foundation: no persistent address, no persistent profile. If the signup matters long-term, use a forwarding alias instead of your primary address — same principle, longer lifespan.
Layer 2: Block remote images by default. Every major email client lets you stop loading remote images automatically — in Gmail it's Settings → Images → "Ask before displaying external images"; Apple Mail and Outlook have equivalents. With images blocked, the pixel never fires, because your client never requests it. You can still load images per-message for senders you trust. This single setting defeats every tracking pixel ever made, regardless of whose address you used.
Layer 3: Turn on the platform protections. If you use Apple Mail, enable Mail Privacy Protection. If you use Gmail, know that its image proxy already masks your IP and location from senders. These don't replace layers 1 and 2, but they shrink what a firing pixel can report.
Layer 4: Never "unsubscribe" from mail you didn't request. Legitimate commercial email in the US must include a working unsubscribe mechanism — that's the CAN-SPAM Act of 2003, and it's the law. Use it for companies you actually did business with. But for true unsolicited spam, clicking unsubscribe is a liveness signal to the spammer. Mark it as spam, or if it went to a temp address, do nothing at all and let the address expire.
Layers 1 and 2 together are the whole game for most people. The pixel can't phone home if the image never loads, and it can't build a profile if the address doesn't survive the week.
What temp email can't do about pixels
Honesty requires the limits, too. A temp email does not make you invisible while you're actively using it.
If you open a marketing email inside your temp inbox with images enabled, the pixel fires in real time and the sender learns everything in the five-point list above — for that session. The defense is that the data has nowhere to accumulate, not that the single open is hidden. If real-time open data on one campaign worries you, that's what layer 2 (image blocking) is for.
Similarly, temp mail does nothing about tracking in the channels it doesn't touch: the pixels in order confirmations sent to your real address, the read receipts in your work email, the tracking in messaging apps. Disposable email is a perimeter defense for the addresses you hand out, not a cloak for the identity you live in. Use it where it works — signups, marketing, anything optional — and don't expect it to cover the accounts tied to your real life.
And one caution that applies to every privacy tool: a temp inbox that anyone can open is worse than no temp inbox at all. If you're reading sensitive mail in a disposable address, make sure the inbox itself is private. The pixel conversation is moot if a stranger is reading the same messages.
FAQ
Can senders track me if I never open their emails?
Mostly no. The pixel fires on open (image load), so an unopened email reports nothing back. The exception is pre-fetching: some clients download images in the background for emails you haven't opened. Apple Mail Privacy Protection specifically counters this by pre-loading everything privately.
Does Gmail's image proxy mean I'm safe from tracking?
Safer, not safe. Since 2013, Gmail serves images through its own servers, so senders don't get your IP address or location. But they still see that you opened the email, when, and how many times. The open itself is still tracked — only the location and network details are masked.
Is email tracking legal?
In most jurisdictions, yes, when it's done by a company you gave your address to — it's typically covered by the privacy policy you accepted at signup. That doesn't mean you have to accept the tracking itself: blocking remote images and using disposable addresses are entirely legitimate responses. Using a temp email is legal; so is choosing not to load someone's spy pixel.
Do tracking pixels work in plain-text emails?
No. Plain-text emails can't load remote images, so there's nothing to fire the pixel. If you set your client to display mail as plain text, you defeat tracking pixels completely — at the cost of ugly, unformatted email. Blocking remote images in HTML view is the better trade-off for most people.
I clicked 'unsubscribe' on obvious spam. Did I just make it worse?
Possibly. For legitimate companies, unsubscribe works as intended. For actual spammers, the click confirms your address is active and monitored, which can increase the volume. When in doubt, mark it as spam instead — and next time, give that kind of signup a disposable address so there's nothing to unsubscribe from.
---
The tracking pixel is a perfect little parable about the modern internet: a feature, not a bug, built by respectable companies, operating entirely in the open, converting your casual reading into someone else's inventory. You don't need to defeat it with technology wizardry. You defeat it with ephemerality — an address that doesn't survive long enough to be profiled — and a single settings toggle that stops the image from loading in the first place. The spy in your inbox only has power while you stand still. So don't.