


Phishing Is Out of Control — Here's How to Fight Back
A phishing reporting tool is a software platform or service used to flag, analyze, and initiate the takedown of malicious emails and websites. These tools are essential for disrupting cybercriminal infrastructure and protecting users from credential theft.
| Tool | Best For | Cost |
|---|---|---|
| PhishTank | Community-driven URL verification | Free |
| OpenPhish | Automated real-time phishing intelligence | Free/Paid |
| Google Safe Browsing | Reporting phishing URLs to Google | Free |
| Phish Report | Professional takedowns and brand protection | Free trial/Paid |
| NINJIO ALERT | One-click employee email reporting | Paid |
| APWG | Forwarding phishing emails for analysis | Free |
Phishing is not slowing down. Attacks increased 31% year-over-year, and phishing now accounts for over 36% of all data breaches. The FBI recorded more than $1.4 billion in losses from phishing and email scams in the US alone in a single year.
And it's not just big companies at risk. 83% of organizations experienced a phishing attack last year. Individuals are targeted just as often — sometimes more.
The scary part? One phishing link is all it takes. A fake login page. A spoofed email. A domain that looks almost right — like paypall.com instead of paypal.com. Blink and you miss it.
That's exactly why having the right phishing reporting tool in your corner matters. Reporting phishing doesn't just protect you. It helps take dangerous sites offline, warns others, and feeds global threat intelligence systems that make the internet safer for everyone.
This guide breaks down the best tools available, how each one works, and how to use them effectively — whether you're an individual protecting your inbox or a security team managing brand impersonation attacks at scale.
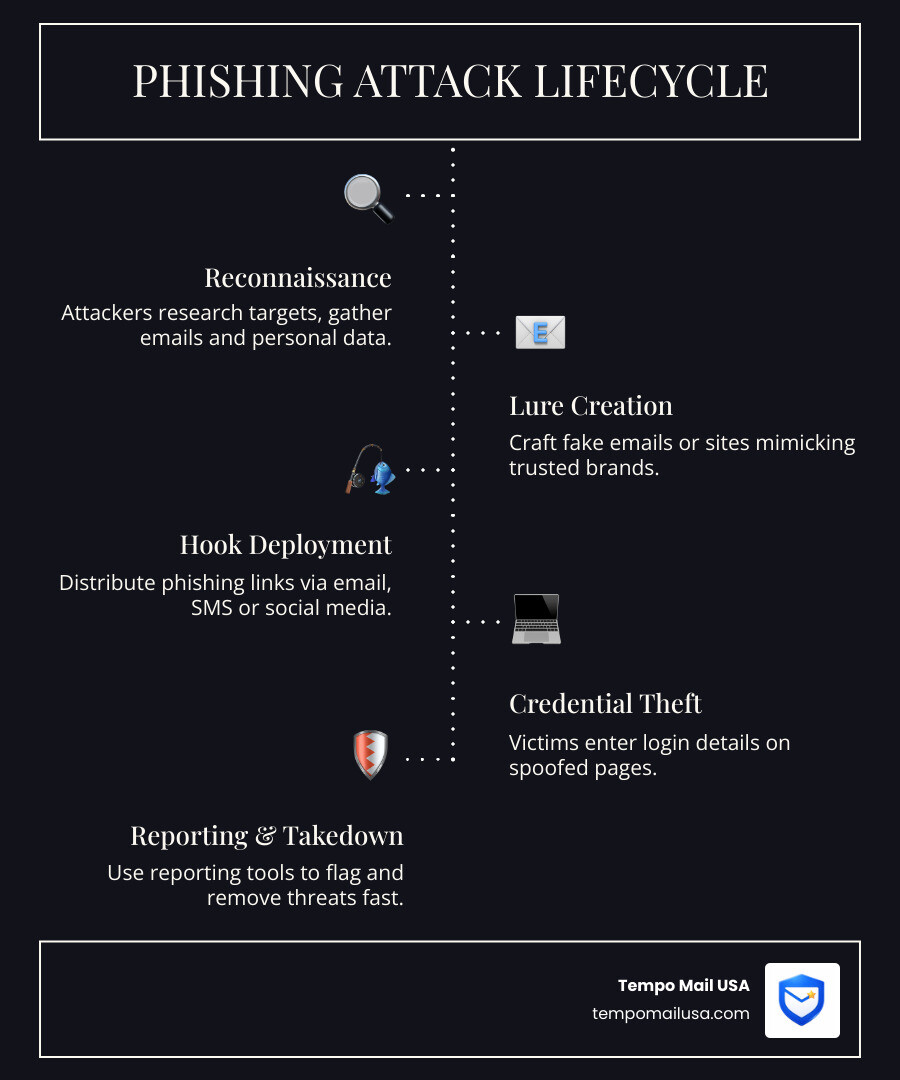
Why Every Organization Needs a Phishing Reporting Tool
Organizations use phishing reporting tools to reduce data breach risks, automate threat analysis, and empower employees to act as security sensors. When the stakes involve millions in potential losses, a simple "delete" button is an insufficient defense strategy.
Every organization, regardless of size, needs a dedicated phishing reporting tool because phishing attacks account for over 36% of all data breaches. When an employee reports a suspicious email, they aren't just deleting trash; they are providing "ground truth" intelligence that can save the company millions.
The APWG Q3 Trends Report highlights that these scams are rising across different vectors, including mobile apps and social media. By implementing a formal reporting tool, we empower employees to move from being "targets" to being "sensors."
Key Benefits of Phishing Reporting Tools:
- Rapid Incident Response: Reduces the "dwell time" of a threat in your environment.
- Financial Protection: Prevents costly Business Email Compromise (BEC) and wire fraud.
- Global Herd Immunity: Your report helps block the site for everyone else on the internet.
- Employee Engagement: Builds a "security first" culture where everyone feels responsible for the perimeter.
- Data Enrichment: Provides security teams with the headers and URLs needed to perform deep forensics.
Top Features of an Effective Phishing Reporting Tool
Not all tools are created equal. If we're looking to truly disrupt an attacker's operations, we need features that go beyond a simple "flag" button.
- Automated Analysis: Tools like OpenPhish use fully automated platforms to identify phishing sites in real-time without needing human intervention.
- Takedown Guidance: Professional tools like Phish Report provide step-by-step instructions on how to contact hosting providers.
- Verified Abuse Contacts: Instead of relying on generic (and often outdated) WHOIS data, top tools maintain databases of verified abuse contacts for faster response.
- Evidence Screenshots: A high-quality phishing reporting tool will use a real Chrome browser to take screenshots of the malicious site. This is crucial because many phishing kits use "cloaking" to show a fake Chrome error page to automated scanners while showing the real scam to actual victims.
- Anti-Analysis Bypass: Advanced tools can detect and bypass the tricks scammers use to hide from security researchers.
How a Phishing Reporting Tool Integrates with Security Workflows
A tool is only useful if people actually use it. This is why integration is key. Most modern tools offer email client add-ins (like the Phish Alert Button) that live right in Outlook or Gmail. One click, and the email is gone from the inbox and sent to the security team for review.
For security professionals, these tools often include API integrations and case collaboration features. This allows teams to track the Master How to Spot Phishing Emails workflow, tag specific threat actors, and monitor the timeline of an attack from the moment a domain is registered to the moment it is suspended by the host.
Community vs. Professional Phishing Detection Platforms
Phishing detection platforms generally fall into two categories: community-driven crowdsourcing and professional automated intelligence. Both are essential parts of the global security ecosystem.
PhishTank: The Community Powerhouse
PhishTank is a community-driven platform where users submit suspected phishing URLs. Other users then vote to verify if the site is indeed a "phish." Once verified, this data is shared via a free API with developers and security companies worldwide. It’s a brilliant example of "crowdsourced" security.
OpenPhish: The Automated Specialist
OpenPhish takes a different approach. It receives millions of unfiltered URLs from a global partner network and uses automated intelligence to extract metadata. It identifies targeted brands, phishing kits, and even the "drop accounts" where stolen credentials are sent.
Google Safe Browsing
When you report phishing to Google Safe Browsing, you are feeding one of the largest security systems on the planet. Google uses these reports to improve its automated detection. While they might not take direct action against every individual site reported, these submissions play a massive role in protecting billions of Chrome and Gmail users.
| Feature | Community (e.g., PhishTank) | Professional (e.g., Phish Report) |
|---|---|---|
| Verification | Human voting/consensus | Automated signatures & IOK language |
| Speed | Depends on community activity | Real-time / Immediate |
| Takedown Support | Minimal (provides data only) | Step-by-step guided takedowns |
| Metadata | Basic (URL, Target) | Deep (Kit info, hosting provider, timeline) |
| Primary User | Individuals & Developers | Enterprise Security Teams |
How to Use a Phishing Reporting Tool for Maximum Impact
To use a phishing reporting tool effectively, you must provide actionable evidence such as technical headers and original URLs. Reporting a phish is more than just hitting a button; it's about ensuring the data is actionable for security teams.
- Forward as Attachment: This is the "gold standard" for reporting. Simply forwarding an email can strip away the technical headers that security teams need. By using "Forward as Attachment," you preserve the original metadata.
- Use APWG Standards: You can forward suspicious emails to reportphishing@apwg.org. This contributes to a global archive used by law enforcement and security researchers.
- Preserve the URL: If you find a phishing site in search results, use the Google Report Phishing form.
- Track the Timeline: If you are using a professional tool like Phish Report, don't just send the report and forget it. Track the timeline. If the site is still up after 24 hours, use the tool's guidance to follow up with the hosting provider.
- Evidence Preservation: Take screenshots (or let your tool do it for you). This is vital if the site goes offline before an investigator can see it.
Best Practices for Detecting and Disrupting Phishing Campaigns
Detecting phishing requires a 'Stop, Look, and Think' approach, focusing on link verification, domain spelling, and multi-factor authentication. Before you can report a phish, you have to spot one.
- Link Hovering: Always hover your mouse over a link before clicking. Does the destination URL match the text? If a "Microsoft" link points to a string of random numbers or a strange domain like
wiizairlines.com.ru, it's a trap. - Check for Misspellings: Look for "look-alike" domains. Scammers love using
rnicrosoft.com(using 'r' and 'n' to look like an 'm') orpaypall.com. Our Quick Guide: How to Spot Phishing Emails covers these visual tricks in detail. - Signature Languages: Professional teams use open-source languages like IOK (Indicators of Kit) to classify phishing kits. This helps them find variants of the same attack across the web.
- Beware of Fake Error Pages: If a site looks like a "404 Not Found" page but asks you to "Verify your identity" to see the content, it’s likely using cloaking to hide from a phishing reporting tool.
- Layer Your Defense: While reporting is great, prevention is better. MFA prevents over 99% of account compromise attacks. Even if you accidentally give away your password, MFA can act as the final lock on the door.
- Proactive Privacy: Use email aliases. At Tempo Mail USA, we believe the best way to Stop Phishing: Effective Strategies to Prevent Attacks is to never give out your real email address in the first place. If an alias starts receiving phish, you can simply delete the alias without affecting your primary inbox.
Frequently Asked Questions about Phishing Reporting
What is the best free phishing reporting tool for individuals?
The best free phishing reporting tools for individuals are PhishTank and Google Safe Browsing. While built-in reporting features in Gmail or Outlook are the first line of defense, these platforms allow you to contribute to global security by submitting malicious URLs directly to shared blocklists.
How do I track the status of my phishing report?
You can track report status through user dashboards on platforms like PhishTank or Phish Report. Community platforms like PhishTank show how many users have verified your submission, while professional tools like Phish Report provide a detailed case timeline showing when the host was notified and when the site was taken down.
Does reporting a phishing site actually lead to a takedown?
Yes, reporting a phishing site triggers the legal and technical processes required for a takedown. Security teams using professional tools take down thousands of sites weekly. While response times vary by hosting provider, reporting is the only way to ensure malicious content is removed from the internet.
Conclusion: Building a Culture of Proactive Defense
Phishing is a numbers game. Attackers send out millions of lures, hoping just one "big one" gets away with the loot. By using a phishing reporting tool, we flip the script. We turn every recipient into a defender.
At Tempo Mail USA, we advocate for a "firewall" approach to digital identity. By using secure email aliases to proxy your identity, you shield your real PII (Personally Identifiable Information) from services. If a service you use is breached and the attackers start sending phishing emails, they only have your alias—which you can kill with a single click.
Combined with a proactive reporting habit, this strategy makes you a very difficult target. Don't just delete that suspicious email—report it, track it, and help us take it down. For more tips on staying safe, check out our guide on Report Phishing Attack: Your Guide to Outsmarting scammers. Stay safe out there!