Reusing the Same Temp Email Everywhere: The Shortcut That Rebuilds Your Profile
The address I kept reusing, and the inbox that gave me away
For about a year, I had a system I was quietly proud of. One disposable address, memorized, pasted into every signup that did not deserve my real inbox. A coupon here, a forum there, a game beta, a store loyalty card, a free trial I planned to cancel. It felt disciplined. My real inbox stayed clean, and the disposable one absorbed everything else. When friends complained about spam, I would explain my system like a man describing a well-organized garage.
Then one of those services had a rough week. A breach notice arrived, the kind written in the passive voice companies use when they would rather you did not read past the first paragraph. It listed the exposed fields: names and email addresses, it said, nothing financial. I shrugged, because the address was disposable and the name was barely a name. Then I did the arithmetic I had been avoiding. That same address was attached to roughly forty accounts. Not forty versions of me. Forty accounts that all pointed, cleanly and unambiguously, to the same string of characters, and through it, to each other.
Nothing catastrophic happened. No account was taken over, no money moved, no embarrassing message surfaced. That is precisely why this habit is dangerous: the damage from reusing a temp email is usually not a single dramatic event. It is a slow accumulation of linkages, each one harmless on its own, that together rebuild the very profile the disposable address was supposed to prevent. A temp email is a wall. A reused temp email is a wall with a single door in it, and every service you hand the address to gets a copy of the key.
My position, after untangling that year of signups, is blunt. A disposable address you use once, or for one purpose, is one of the best privacy tools an ordinary person has. A disposable address you use everywhere is a second permanent identity, except worse: it carries all the linkability of a real address and none of the recovery options, because the day you abandon it, every account tied to it becomes an account you can no longer prove you own.
The convenience trap: why one address feels smarter
Reusing feels smart for reasons that are entirely real, and dismissing them would be dishonest. A single address is easy to remember. You never stand in a store aisle wondering which of your dozen disposable inboxes holds the coupon code. Password resets go to one place. When a service asks you to confirm your email, you know exactly where to look. Compared with the chaos of a fresh address per signup, one address feels like the grown-up version of the habit.
It also feels safer than the alternative most people actually practice, which is handing out their real address. Against that baseline, a single disposable address is a genuine improvement. Your bank statements are not in that inbox. Your employer cannot see it. Your family photos are not attached to it. If your standard is "better than my real email," one temp address passes easily, and that is why so many careful people stop there.
The trap is that the comparison is wrong. The question is not whether a reused temp email beats a real email. It is whether a reused temp email still does the job you bought it for, and that job has two parts, not one. The first part is keeping junk out of your real inbox. A reused temp email does that perfectly. The second part is keeping your signups from being connected to each other. A reused temp email fails that part completely, because connection is exactly what a shared identifier does. Every privacy guide that takes this seriously lands in the same place: generate a separate address per service, because a leak at one service stays contained only if no shared identifier links it to the others. The convenience you gain by reusing is paid for with the one property that made the tool worth using.
There is a second, quieter convenience at work too. A single address lets you avoid deciding. Each new signup with a fresh address forces a small judgment: is this a throwaway, a trial I might keep, or something that needs a stable contact? Reusing skips the judgment. That is appealing, and it is also how a coupon signup and a health-adjacent account end up sharing an address, which is a pairing no one would choose deliberately. The shortcut does not just connect your accounts. It connects them without your attention, which is the worst way for a privacy decision to be made.
One address becomes a map of your life
Think about what an email address actually is to the companies that hold it. It is not just a delivery route for messages. It is the most reliable join key in consumer data. Names vary, phone numbers change, cookies get cleared, devices get replaced. An email address, especially one a person keeps for years, stays stable across all of that, and data systems are built to exploit stability. When the same address appears in a shopping account, a forum, a fitness app, a game, and a travel booking, each of those services, and any data broker that buys from them, can draw a line between those activities and conclude they belong to the same person.
You do not need a conspiracy to explain this. You need only the ordinary mechanics of the modern web: signup forms, order confirmations, newsletter lists, breach compilations, and the data trade that stitches them together. The shopping service knows what you buy. The forum knows what you argue about. The fitness app knows when you exercise. None of them knows your real name, perhaps, but they do not need it. The shared address is enough to assemble a profile with your tastes, your schedule, your location hints, and your spending, and that profile is attached to an identifier you chose precisely because you thought it revealed nothing.
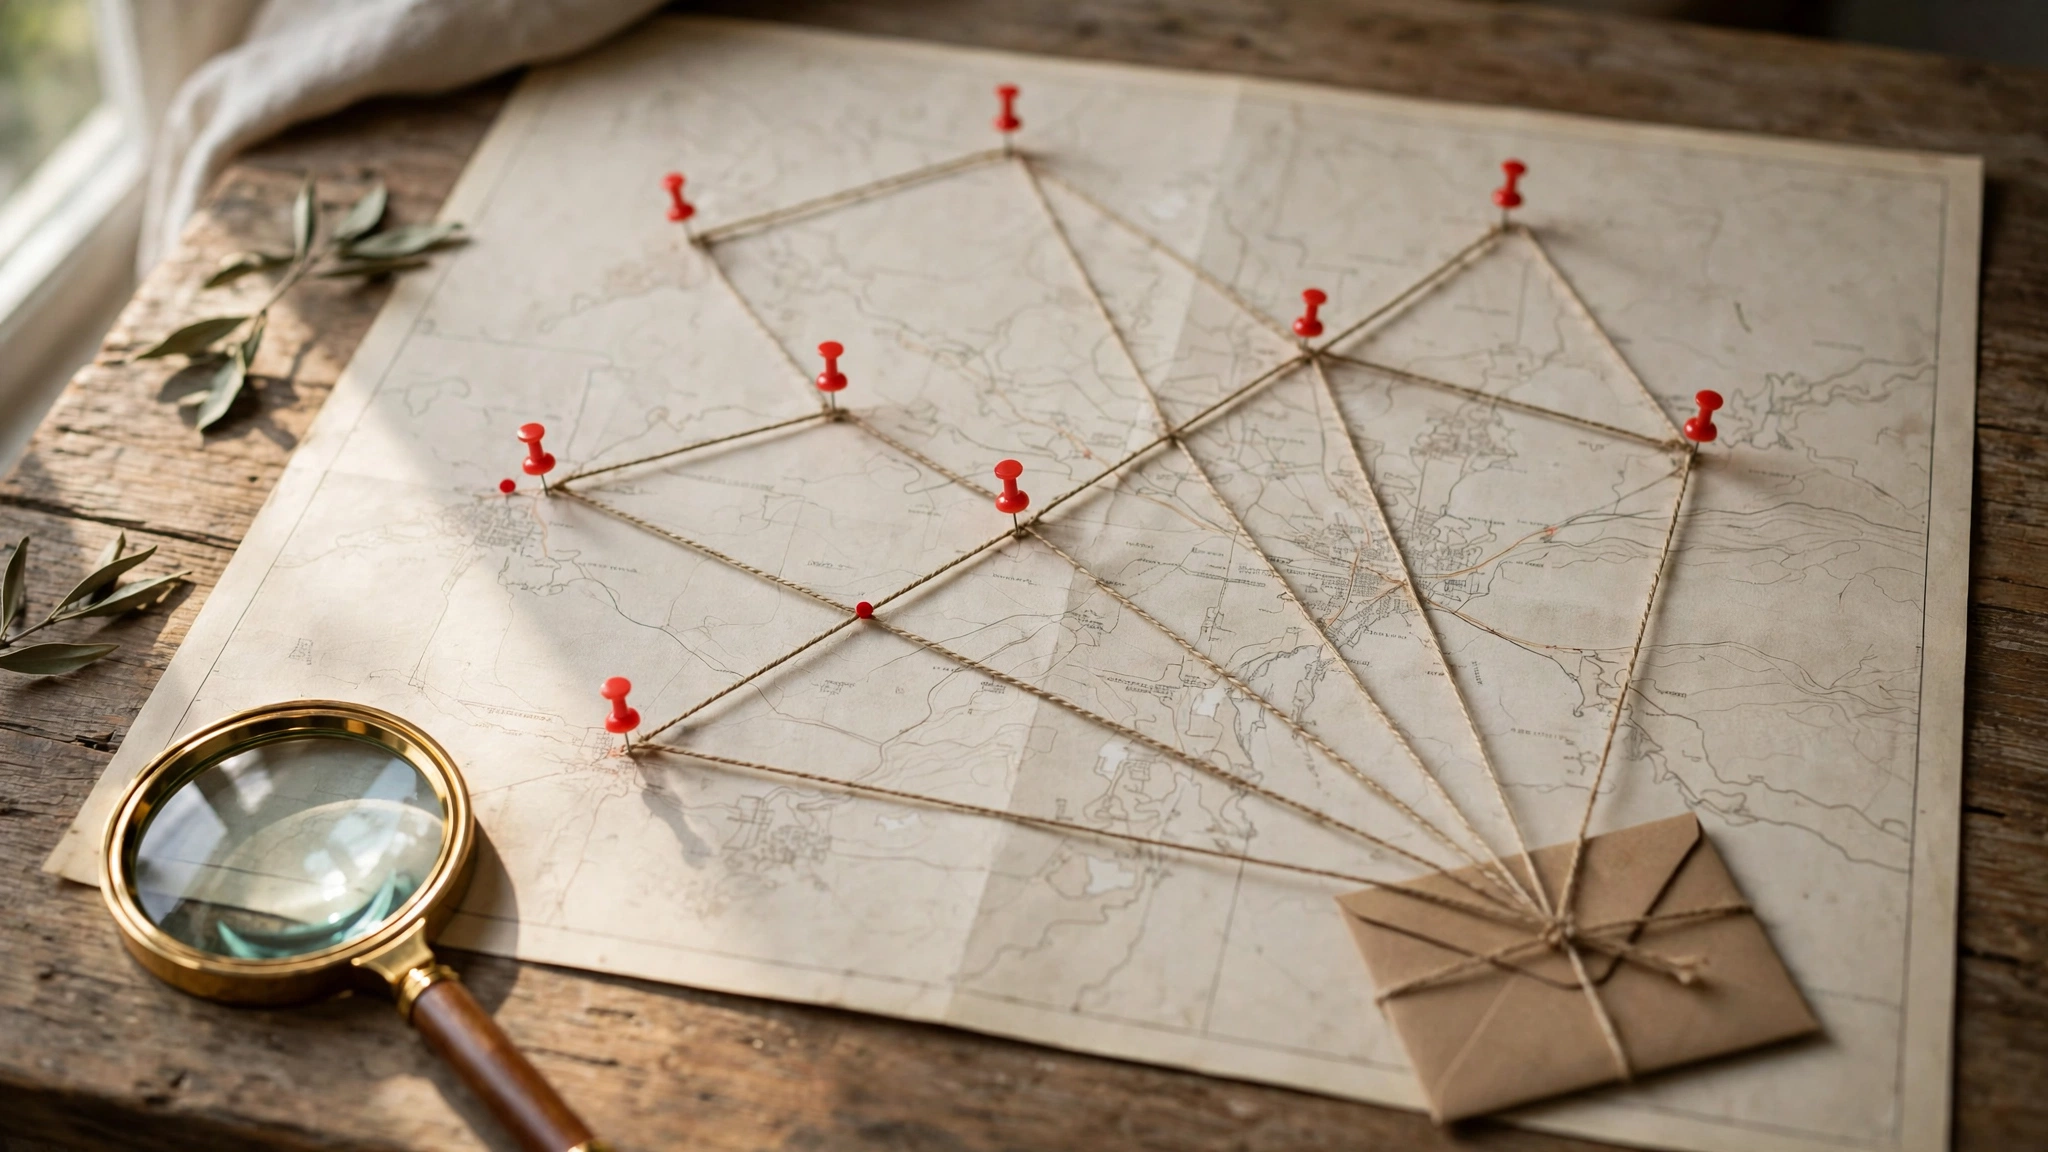
The map metaphor is useful because it shows why partial damage is still damage. Losing one pin on a map tells an observer little. Losing forty pins, all tied by string to the same envelope, tells them the shape of a life: where you shop, what you play, what you read, where you travel, what you worry about at 2 a.m. when you sign up for a sleep app. A temp email was supposed to scatter those pins across forty envelopes. Reusing one address gathers them back into a single pile, neatly labeled, and hands the pile to anyone who ever gets hold of it, legitimately or not.
This is also why the "but it's not my real name" defense is weaker than it feels. Anonymity is not the same as unlinkability. An address that reveals no name still reveals a pattern, and patterns are what modern profiling runs on. A pseudonymous profile that knows your purchases, your hobbies, and your routines is not anonymous in any sense that matters to an advertiser, a data broker, or a scammer assembling a phishing attempt. The scammer does not need your legal name to write a convincing message. They need to know you use a particular game, shop at a particular store, and recently booked a particular kind of trip, and a reused address hands them all three in one place.
A breach in one place becomes a key everywhere
The sharper risk is not profiling. It is recovery. Email addresses are the master key for most consumer accounts, because password resets flow through them. When one address is the recovery address for forty accounts, a compromise of that one inbox, or even of one service that holds it, changes the geometry of an attack. The attacker does not need to break into forty accounts. They need to find the one thread that connects them, and then pull.
Start with the simplest version. A service you signed up for with your reused address suffers a breach, and the exposed data includes your address plus some hint of who you are on that service. On its own, that is a minor exposure. But the address is also your login or recovery address on a dozen other services, several of which you have forgotten you joined. A credential-stuffing attempt, a phishing email that references a real service you actually use, or a password reset request all become easier, because the attacker is no longer guessing which services you use. Your reused address is a directory of them.
The deeper version is the recovery chain, and it deserves a plain telling because it is the mechanism people miss. Many of us secure our important accounts with a recovery email, and then secure that recovery email with another address, and so on, until the chain ends somewhere we chose casually years ago. A disposable address reused across dozens of signups is an ideal weak link in such a chain: it looks unimportant, so it gets a weak password, no second factor, and no attention, while quietly sitting upstream of accounts that matter. The full argument, with the chain laid out step by step, is in our piece on how one email becomes the key to all your accounts, and it is worth reading before you decide your reused address is low-stakes. The address is only low-stakes if nothing important is downstream of it, and with forty accounts attached, something almost certainly is.
There is a related failure that is less dramatic but more common: expiry. Disposable addresses are meant to be abandoned, and some services delete them after a period of inactivity. If your reused address expires or you lose access to it, you do not lose one account. You lose the recovery path for all forty at once, and you discover the loss one password reset at a time, usually at the worst moment. The same logic that makes a single point of failure dangerous in engineering makes it dangerous in identity: the convenience of one address is the fragility of one address, and the bill arrives all at once.
The quieter damage: profiling, cross-site matching, and the unsubscribe that never works
Beyond breaches, reuse degrades the everyday experience in ways that are easy to misdiagnose. The first symptom is usually the unsubscribe that never works. You unsubscribe from a store's mail, and similar mail keeps arriving, because the list you left is not the only list that holds your address. A partner, a co-sponsor, or a data append has the same string, and each new sender treats it as a fresh consent. With a separate address per service, the culprit is obvious: the address that is suddenly noisy tells you exactly which signup leaked or sold it. With one reused address, every sender is indistinguishable, and you cannot tell a leak from a legitimate list you forgot. You lose the diagnostic power that is, in my view, the single most underrated benefit of disposable mail.
The second symptom is targeting that feels uncannily specific. You sign up for a running app with your reused address, and within weeks the shopping service that shares that address starts showing you running gear, because a data partner matched the two records on the shared key. Nobody hacked anything. Two legitimate businesses, or their vendors, joined records on an identifier you provided to both. This is the mechanism behind much of the "how did they know?" feeling online, and it runs on shared identifiers more than on any exotic tracking technology. Reusing an address donates the join key.
The third symptom is blocklisting with collateral damage. Sites that reject disposable domains, for reasons explained in our guide to why websites reject temp email, often block by domain, not by individual address. But some services also flag or restrict individual addresses with suspicious patterns, and an address that appears in dozens of signups in a short period can look like exactly the kind of bulk or bot behavior those systems are tuned to catch. One flagged address then poisons every account attached to it, instead of one. Separate addresses contain that blast radius to a single signup, which is the entire point of compartmentalization.
None of this requires you to be an interesting target. Data systems do not profile people because they are interesting. They profile everyone, because matching is cheap and the marginal value of one more link is positive. Reusing a temp email does not make you a target. It makes you legible, and legibility is the raw material the whole apparatus runs on.
When reusing is actually fine
A rule with no exceptions is a rule people will ignore, so here are the exceptions, stated plainly. Reusing one disposable address is fine when the accounts it connects are already connected in every other way, and when the address will live only as long as the project it serves.
The cleanest case is a single bounded project. You are organizing a conference, running a short course, testing a product, or signing up for a cluster of services for one trip, and you create one address for that project alone. Every account attached to it belongs to the same endeavor, the address dies when the project ends, and no one account's exposure reveals anything about your life outside the project. That is not reuse in the harmful sense. That is a labeled folder, and it works because the boundary is the project, not the address.
The second case is your own testing. Developers and curious users routinely sign up for their own sites, or for a handful of test accounts, with one disposable address. The accounts are not real parts of your life, the data in them is synthetic, and linking them reveals nothing. The same applies to a throwaway used for a single afternoon of comparison shopping, where every signup is the same task and the address is abandoned the same day.
The third case is a category address, used deliberately rather than by drift. One address for all your newsletter subscriptions, for example, where you have already accepted that the newsletters are one category of your life, and where the address is separate from your shopping, gaming, and health-related signups. This is a compromise, and it should be named as one: you are trading some linkability within a category for manageability. It is far better than one address for everything, and far worse than one per service. The test is whether you could explain the grouping to someone without embarrassment. "All my newsletters" passes. "My bank-adjacent trial, my dating profile, and my grocery coupons" does not.
What does not qualify as an exception is the most common situation: an address that started as a single-purpose throwaway and quietly accumulated forty unrelated signups because it was already memorized and already pasted into the clipboard. Drift is not a decision. If you cannot say, off the top of your head, what your reused address is for, it is not serving a purpose. It is serving inertia, and inertia is the thing that needs replacing.
A separate address per service, without the chaos
The standard advice, one address per service, fails in practice for a boring reason: nobody can remember forty addresses, and the systems for managing them feel heavier than the problem. So here is the version that actually survived contact with my own habits, after the year of reuse ended.
First, stop trying to remember addresses at all. That is the password manager's job, or a single note's job, and the sooner you accept that, the sooner the system works. When I sign up for something now, I generate a fresh address and immediately paste it, alongside the service name, into the same password manager entry as the password. The address is not a thing I memorize. It is a field in a record, exactly like a username. The objection that this is too much work dissolves once you notice that you were already saving the password. You are adding one field to a step you already take.
Second, use categories as a fallback, not a default. If one address per service genuinely feels unmanageable for a batch of low-stakes signups, use one address per category: one for shopping, one for media trials, one for forums, one for coupons. Four addresses are nearly as easy to manage as one, and they cut the linkability by an order of magnitude, because no single address maps your whole life. Categories are a compromise, but they are a compromise with a visible boundary, and visible boundaries are what keep a compromise from drifting into the old habit. When a category grows past a dozen services, split it. That is the rule that prevents categories from becoming the same problem with a new name.
Third, name addresses so future-you can read them. Where the service allows it, the local part of the address can carry a hint: the service, the month, the purpose. Where it cannot, the password manager note carries it. The goal is that six months from now, when a breach notice or a strange email arrives, you can answer one question in ten seconds: which signup does this address belong to? If you cannot answer that question, the address is not a system. It is a mystery, and mysteries are how reused addresses accumulate.
Fourth, treat expiry as a feature, not a threat. For a signup you genuinely do not expect to keep, prefer an address with a short life, and let it die. For a signup you might keep, use an address you control for longer, and write down the date you will revisit it. The distinction matters because it forces the judgment that reuse skips: is this a throwaway, or is this a relationship? Most signups are throwaways pretending to be relationships, and naming them correctly at signup time is half the work. The honest rules for free trials make the same point from the trial side: decide at signup whether you will keep the thing, because deciding later, after the renewal email arrives at an address you no longer check, is not deciding at all.
The 20-minute untangle: moving off a reused address
If you are reading this with a reused address already attached to dozens of accounts, do not try to fix it in one sitting. The untangle works as a short, bounded session, repeated a few times, and it starts with an inventory, not with deletions.
Step one, ten minutes: open the reused inbox and sort it by sender. Do not read the mail. Just list the senders, and mark each one as keep, drop, or unknown. Keep means you still use the service and would miss it. Drop means you do not recognize it, or you recognize it and do not care. Unknown means you need to open one message to decide. Most people find the list is shorter than they feared, because a handful of senders produce most of the mail, and the long tail is services they forgot entirely.
Step two, five minutes: for every keep, decide its new home. Services you genuinely use go to your real address, or to a dedicated category address you control long-term. Services you use occasionally go to a fresh disposable address each, recorded in your password manager. This is the step people skip, and skipping it is how the untangle fails: without a new home chosen in advance, the old address stays the default out of sheer momentum.
Step three, five minutes: change the address on the three most important keeps, and only those three. Log in, change the email, confirm from the new inbox, and update the password manager entry. Three changes per session is enough, because each change has a confirmation step and a waiting step, and batching ten of them is how you end up locked out of something. Repeat the session every few days until the keeps are moved. The drops need no action at all: stop checking the old address, and they fade with it, which is the feature you bought in the first place.
Two warnings belong in this section, because both are mistakes I have watched people make. First, do not delete the old address, or stop checking it, until the important keeps are moved and confirmed. Deleting first and moving second strands every account whose confirmation goes to an address you just killed, and it converts a tidy migration into a support-ticket marathon. Second, do not change the address on an account you cannot currently log into. If you have forgotten the password, recover it first, while the old address still works, and then move it. The order is: access, then move, then abandon. Reversing any two of those steps creates the exact lockout the system was supposed to prevent, and the general rule for when temp email should not be used applies here with full force: anything you might need to recover months later belongs on an address you control permanently, not on one you are in the process of abandoning.
What to do when the reused address is already everywhere
Some readers will have a harder version of this problem: the reused address is not just on newsletters and coupons, but on accounts with money, health information, or professional identity attached, because it was convenient at the time and nobody warned them. The advice changes here, and it changes in one direction: slower, and more conservative.
For any account involving money, health, work, or legal identity, move it to your real address, not to another disposable one, and do it before anything else. The reason is recovery, not privacy. A bank, a health portal, or an employer system will eventually need to reach you about something that matters, and it will need to verify that you are the person on the account. A disposable address, even a fresh one, is the wrong foundation for that relationship, and moving from a reused disposable to a fresh disposable only postpones the problem while adding a migration step. The newsletter signup rules describe the same pattern from the other side: lists find new purposes for your address over time, and the address you gave a coupon site eventually behaves like an identity, whether you intended it to or not.
For accounts you cannot move, because the service does not allow an email change or because you have lost access, contain rather than chase. Enable every second factor the service offers, change the password to a unique one from your password manager, and remove any payment method you no longer use. Then note the account as stranded, with the date, and check the reused inbox for its mail until you are confident nothing important still flows there. Stranded accounts are not a failure of the untangle. They are a normal residue of a habit that ran for years, and the goal is to shrink the residue, not to pretend it can be zeroed in an afternoon.
Finally, set a calendar reminder, one month out, to revisit the old address. Open it once, scan the senders, and ask whether anything important still arrives there. If the answer is no, and the keeps have all been moved and confirmed, you can stop checking it. If the answer is still yes, move the stragglers and set another month. The reminder is the mechanism that prevents the next drift, because drift is what created this problem, and a system without a review step is a system that will drift again. The most honest summary I can offer is this: a temp email is not a permanent identity, and the moment you treat it like one, by reusing it everywhere, it starts behaving like one, with all the exposure and none of the safeguards. Use it the way it was designed to be used, one purpose at a time, and it stays the useful, boring tool it was supposed to be.
Frequently asked questions
Is it bad to reuse the same temp email for multiple signups?
It is not catastrophic, but it defeats the main purpose of disposable mail. A reused address links all your signups together, so a breach, a data sale, or a profiling match at one service exposes the rest. Use a fresh address per service, or at least one per category, so a problem at one signup stays contained to that signup.
Can someone find my real identity from a reused temp email?
Not directly from the address alone, but a reused address makes identification much easier. When the same address appears across shopping, forums, fitness, and travel accounts, the combined pattern often reveals location, habits, and spending, even without a real name. Separate addresses break that pattern into pieces that are far harder to join.
What happens if my reused temp email expires?
You lose the recovery path for every account attached to it at once. Password resets, security alerts, and confirmation emails all go to an address you can no longer open. Move important accounts to a permanent address before abandoning a reused one, and recover any account you cannot log into while the old address still works.
Is one temp email per category good enough?
For most people, yes, as a practical compromise. One address per category, such as shopping, media trials, and forums, is far better than one address for everything, because no single address maps your whole life. One address per service is still stronger, and worth it for anything sensitive, but categories are a workable system if you split a category once it grows past a dozen services.
Should I use a temp email for accounts with money or health information?
No. Accounts involving money, health, work, or legal identity need an address you control permanently, because you will need to recover them and verify your identity months or years later. Use a temp email for low-stakes signups you can walk away from, and your real address for anything you would miss if it disappeared.
How do I switch accounts off a reused temp email?
Inventory first: list the senders in the old inbox and mark each as keep or drop. For each keep, choose its new home in advance, then change three accounts per session, confirming each move from the new inbox before moving on. Do not delete or stop checking the old address until the important accounts are moved and confirmed.
Does reusing a temp email make spam worse?
It makes spam harder to diagnose and harder to stop. With one address everywhere, you cannot tell which signup leaked or sold it, and unsubscribing from one list does not stop partners and data appends that hold the same address. A separate address per service tells you immediately which signup is responsible when a new wave of mail starts.
Is a reused temp email still better than my real email?
For keeping junk out of your real inbox, yes. For keeping your signups unlinkable, no. It is a partial improvement that feels like a complete one, which is why it is so common. If you want the full benefit of disposable mail, the address has to be disposable in practice, not just in name, and that means not reusing it across your whole digital life.
Need a disposable temporary email?
Protect your real inbox from spam and promotional clutter instantly and free.
Received a suspicious email, text, or charge alert?
Verify whether the sender domain is disposable, spoofed, or unverified before clicking links.